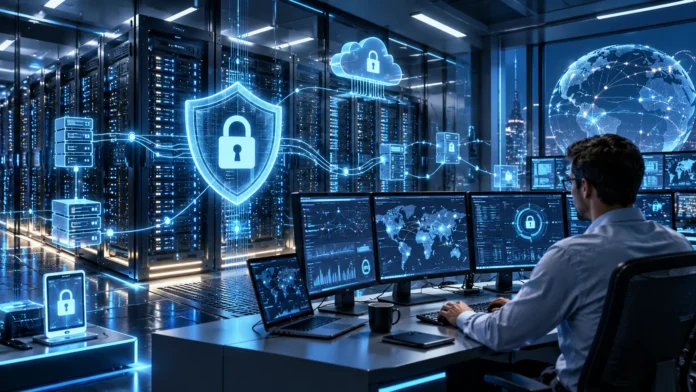
Cybersecurity infrastructure is the foundation of modern digital security, helping organizations protect their networks, systems, applications, and sensitive information from cyber threats. As businesses increasingly depend on cloud computing, digital communication, and connected devices, maintaining a secure IT environment has become essential. A well-designed security infrastructure helps prevent unauthorized access, reduce operational risks, and support business continuity.
Cyberattacks can affect organizations of every size, from small businesses to multinational corporations. Threats such as ransomware, phishing, malware, and data breaches can disrupt services, compromise confidential information, and create significant financial losses. Cybersecurity infrastructure brings together security technologies, policies, skilled professionals, and monitoring processes to reduce these risks.
Understanding how cybersecurity infrastructure works helps businesses make informed decisions about protecting their digital assets. This guide explains its meaning, essential components, different types, common threats, implementation strategies, and future developments. It also explores practical ways organizations can strengthen their security posture while supporting reliable business operations.
What Is Cybersecurity Infrastructure? Meaning and Definition
Cybersecurity infrastructure refers to the collection of technologies, security systems, policies, and operational processes used to protect an organization’s digital environment. It includes network security devices, endpoint protection software, identity management systems, monitoring tools, and data protection mechanisms. These components work together to reduce cyber risks, identify suspicious activities, and maintain the confidentiality, integrity, and availability of information.
Unlike individual security applications, cybersecurity infrastructure provides a coordinated approach to protecting interconnected digital assets. A business may use firewalls to control network traffic, encryption to protect confidential information, and authentication systems to verify user identities. When these measures are properly integrated, they establish multiple security layers that help prevent isolated vulnerabilities from compromising the entire environment.
The meaning of cybersecurity infrastructure extends beyond installing software or purchasing security equipment. Effective protection also depends on trained personnel, clearly defined responsibilities, regular maintenance, and established incident response procedures. Organizations must continuously assess their security requirements because emerging technologies, changing business operations, and evolving cyber threats can introduce new vulnerabilities over time.
Why Is Cybersecurity Infrastructure Important?
Cybersecurity infrastructure is important because businesses increasingly rely on digital systems to manage essential operations and store valuable information. Customer records, financial transactions, intellectual property, and internal communications may all require protection against unauthorized access. A strong security foundation helps reduce exposure to potential attacks while supporting the reliable functioning of business applications and networks.
Another major benefit is improved business continuity during unexpected security incidents or technical disruptions. Protective controls, reliable backups, and incident response procedures can limit damage and support recovery when problems occur. Although no security system guarantees complete protection, properly maintained infrastructure can make attacks more difficult and help organizations respond effectively when defensive measures fail.
Cybersecurity infrastructure also supports customer confidence and helps organizations fulfill applicable privacy and security obligations. Businesses that handle personal or confidential information may need to follow industry-specific regulations and contractual requirements. Maintaining appropriate security safeguards demonstrates responsible information management and reduces the likelihood of preventable incidents that could damage organizational reputation.
Essential Components of Cybersecurity Infrastructure
Network security is a central component of cybersecurity infrastructure because it protects the communication channels connecting devices, users, and business systems. Firewalls, network segmentation, intrusion detection systems, and secure remote access technologies help control digital traffic. These controls can restrict unauthorized connections, identify suspicious network behavior, and reduce opportunities for attackers to move between interconnected systems.
Endpoint security focuses on protecting individual devices such as laptops, desktops, servers, and mobile phones. Antivirus software, endpoint detection and response platforms, device management solutions, and operating system updates contribute to this protection. Because employees frequently access organizational resources through personal or company-issued devices, endpoint security plays an important role in limiting malware infections and unauthorized access.
Identity management, encryption, security monitoring, and backup systems provide additional protection across the digital environment. Identity and access management tools determine which users can access specific resources, while encryption protects sensitive information. Monitoring platforms identify unusual activities, and tested backups support data restoration after accidental deletion, equipment failures, or certain security incidents.
How Does Cybersecurity Infrastructure Work?
Cybersecurity infrastructure works by combining preventive, detective, and corrective security controls into a coordinated defense strategy. Preventive technologies attempt to block unauthorized activities before damage occurs, while detection systems monitor environments for suspicious behavior. Corrective procedures help organizations contain incidents, restore affected services, and reduce the likelihood of similar problems happening again.
Consider an employee attempting to access a company’s internal application from a remote location. An identity management system can verify the employee’s credentials and require multifactor authentication before granting appropriate permissions. Network security controls may inspect the connection, while monitoring software records relevant activity and detects unusual patterns that could indicate compromised credentials.
When suspicious activity is identified, security tools may generate alerts or trigger predefined protective responses. Security analysts investigate the available information to determine whether an actual threat exists and what actions are necessary. Depending on the incident, response measures may include isolating affected devices, disabling compromised accounts, applying security updates, or restoring verified data backups.
Different Types of Cybersecurity Infrastructure
On-premises cybersecurity infrastructure protects systems and equipment located within facilities controlled by an organization. Businesses using this approach may operate their own servers, network appliances, security monitoring platforms, and data storage systems. On-premises environments offer direct control over many technical resources but require internal expertise, regular maintenance, and appropriate physical security measures.
Cloud cybersecurity infrastructure protects applications, information, and workloads hosted through cloud computing platforms. It may include cloud security posture management, identity controls, encryption, workload protection, and centralized monitoring services. Responsibility for protecting cloud environments is generally shared between the provider and customer, with specific duties depending on the service model and contractual arrangements.
Hybrid cybersecurity infrastructure combines protection for on-premises systems and cloud-based resources within a connected digital environment. This model is common among organizations that maintain traditional business applications while adopting modern cloud services. Effective hybrid security requires consistent access policies, clear asset visibility, integrated monitoring, and secure communication between different infrastructure environments.
Network Security Infrastructure and Its Key Functions
Network security infrastructure protects the systems and connections that support communication across an organization’s digital environment. Its primary functions include controlling traffic, preventing unauthorized access, detecting suspicious behavior, and limiting potential attack paths. Network security is particularly important because compromised connections can expose multiple applications and devices rather than affecting only one system.
Firewalls are widely used network security tools that evaluate traffic according to defined security rules. Intrusion detection systems identify potentially malicious activities, while intrusion prevention systems may block traffic matching suspicious patterns. Organizations also use virtual private networks, secure gateways, and network access controls to protect communication and regulate connections from remote users or unfamiliar devices.
Network segmentation strengthens infrastructure security by separating resources into smaller, controlled environments. For example, an organization may isolate guest wireless access from sensitive financial systems or production servers. This approach can reduce the opportunities available to attackers after an initial compromise and make security policies easier to apply according to business requirements.
Cloud Security Infrastructure and Data Protection
Cloud security infrastructure protects digital resources hosted in public, private, and hybrid cloud environments. Businesses increasingly depend on cloud services for data storage, collaboration, software applications, and scalable computing resources. Appropriate security controls help protect these services against unauthorized access, configuration errors, exposed information, and other risks associated with cloud technology.
Identity and access management is particularly important in cloud environments because users and applications frequently access resources through internet-based connections. Organizations can strengthen protection through multifactor authentication, least-privilege permissions, secure configuration management, and continuous activity monitoring. Encryption also helps protect confidential data during transmission and storage when properly implemented and supported by secure key management.
Cloud security requires continuous oversight because infrastructure settings, user permissions, and application workloads can change frequently. Automated configuration assessments and vulnerability management tools can identify weaknesses before they create serious exposure. Organizations should also understand their cloud provider’s security responsibilities, maintain appropriate backups, and establish recovery procedures for critical applications and information.
Identity and Access Management in Cybersecurity Infrastructure
Identity and access management, commonly called IAM, controls how individuals and digital services access organizational resources. It establishes processes for identifying users, verifying their identities, granting permissions, and reviewing access privileges. Effective IAM helps protect confidential information by ensuring that only authorized accounts can perform actions permitted by their assigned responsibilities.
Multifactor authentication is an important identity security measure because it requires additional verification beyond a password. Depending on the implementation, users may confirm access through an authenticator application, a security key, or another approved method. This additional protection can reduce the likelihood of unauthorized account access when passwords are stolen, reused, or exposed through phishing.
The principle of least privilege further strengthens security by limiting access to the resources necessary for specific tasks. Organizations should review permissions regularly and remove unnecessary access when responsibilities change or employees leave. Privileged access management solutions provide additional oversight for administrator accounts that control sensitive systems and critical infrastructure components.
Endpoint Security Infrastructure and Device Protection
Endpoint security infrastructure protects devices connected to organizational networks and digital services. These devices frequently interact with email, websites, business applications, and external files, making them potential entry points for cyber threats. Strong endpoint protection helps detect malicious software, reduce unauthorized activities, and prevent compromised devices from creating broader security problems.
Endpoint detection and response solutions continuously collect relevant device activity to identify suspicious behavior and support investigations. Traditional antivirus applications primarily focus on recognizing and blocking malicious software, while modern endpoint platforms can provide broader behavioral monitoring. Device encryption, secure configurations, and timely software updates further reduce exposure to common vulnerabilities and unauthorized information access.
Organizations should establish clear policies for managing both company-owned devices and approved personal equipment. Security requirements may include automatic updates, screen locking, approved applications, and procedures for reporting lost devices. Centralized device management can help maintain consistent security settings and improve visibility across distributed teams and remote working environments.
Common Cybersecurity Threats to IT Infrastructure
Malware remains a significant threat to cybersecurity infrastructure because malicious programs can disrupt systems, steal information, or provide attackers with unauthorized access. Ransomware is particularly concerning because it can interfere with business operations and make important data temporarily unavailable. Layered security controls, staff awareness, and reliable backup procedures help organizations reduce potential damage.
Phishing and credential theft target the people and authentication systems supporting an organization’s digital operations. Attackers may use deceptive messages, fraudulent websites, or social engineering techniques to obtain sensitive information. Employee training, phishing-resistant authentication methods, and suspicious activity monitoring can reduce these risks, although individual awareness should never be the organization’s only defense.
Other important threats include software vulnerabilities, insider misuse, distributed denial-of-service attacks, and insecure infrastructure configurations. Attackers may exploit outdated applications, excessive permissions, or exposed services to gain access to sensitive environments. Maintaining accurate asset inventories, applying appropriate patches, and monitoring critical systems help organizations recognize and address weaknesses before they become serious incidents.
Cybersecurity Infrastructure vs. IT Infrastructure
IT infrastructure includes the hardware, software, networks, storage systems, and computing resources that support an organization’s daily technological operations. Its primary purpose is to provide reliable digital services and enable business processes. Servers, databases, communication networks, and business applications are examples of resources commonly managed within an organization’s broader IT environment.
Cybersecurity infrastructure focuses specifically on protecting these resources against unauthorized access, malicious activities, data loss, and operational disruption. It uses security technologies, policies, monitoring processes, and trained professionals to manage risks affecting IT systems. Although both areas rely on similar technologies, cybersecurity infrastructure introduces protective controls designed to preserve the confidentiality, integrity, and availability of digital assets.
The two infrastructures are closely connected because effective security depends on understanding how business technology is configured and operated. A network administrator may prioritize connectivity and performance, while a security specialist evaluates exposure and access controls. Collaboration between IT and security teams helps organizations maintain reliable services without introducing unnecessary vulnerabilities or operational complexity.
Best Practices for Building Secure Cybersecurity Infrastructure
Building secure cybersecurity infrastructure begins with understanding which systems, applications, and information require protection. Organizations should maintain an updated inventory of their digital assets and evaluate potential threats based on business importance. Risk assessments help identify weaknesses, prioritize necessary controls, and allocate resources according to the potential consequences of different security incidents.
Applying layered security is another essential practice because individual tools cannot protect against every possible threat. Organizations can combine strong authentication, network segmentation, endpoint protection, encryption, and continuous monitoring to establish overlapping safeguards. Regular patch management, secure configurations, employee training, and appropriate access restrictions further reduce exposure to common attack methods.
Effective security planning also requires documented incident response procedures and regularly tested recovery capabilities. Businesses should define responsibilities, establish communication processes, and determine how affected systems will be contained and restored. Periodic security assessments, backup restoration exercises, and staff training help confirm that protective measures remain effective as technologies and organizational requirements evolve.
Zero Trust Architecture in Modern Cybersecurity Infrastructure
Zero Trust is a security approach built around continuously evaluating access rather than automatically trusting users or devices based on network location. Under this model, access decisions consider verified identities, device conditions, resource sensitivity, and applicable security policies. The objective is to reduce unnecessary trust and limit the potential impact of compromised accounts or connected devices.
Identity verification and least-privilege access are fundamental elements of Zero Trust architecture. Organizations may use multifactor authentication, conditional access controls, network segmentation, and continuous security monitoring to strengthen their environments. These measures work together to ensure that access remains appropriate for the requested resource and can be restricted when conditions change.
Implementing Zero Trust usually requires gradual improvements rather than replacing all existing security systems immediately. Businesses can begin by identifying critical resources, strengthening identity protection, and limiting excessive permissions. Over time, integrating additional monitoring and access controls can create a more consistent security model across cloud services, internal networks, remote devices, and business applications.
The Role of Artificial Intelligence in Cybersecurity Infrastructure
Artificial intelligence is increasingly used within cybersecurity infrastructure to analyze large volumes of security data and recognize unusual activity patterns. Machine learning models can help identify potentially malicious behavior across networks, devices, and user accounts. These capabilities may support faster threat detection and reduce some manual analysis requirements for security teams managing complex environments.
AI-powered security tools can also assist with alert prioritization, event correlation, and investigation workflows. By combining information from multiple systems, these platforms may help analysts identify relationships between activities that would otherwise be difficult to notice. However, automated findings still require appropriate validation because inaccurate alerts, incomplete information, and changing attack techniques can affect detection quality.
Organizations should treat artificial intelligence as a supporting technology rather than a complete replacement for skilled security professionals. AI systems require secure configurations, suitable data protection, ongoing evaluation, and human oversight. Combining automation with experienced analysts and established incident response processes helps businesses use advanced detection capabilities while maintaining accountability for security decisions.
How to Maintain and Improve Cybersecurity Infrastructure
Maintaining cybersecurity infrastructure requires regular evaluation of security controls, software configurations, and potential vulnerabilities. Organizations should review system updates, access permissions, monitoring alerts, and asset inventories according to their risk levels. Consistent maintenance helps prevent outdated technology and unnecessary privileges from creating avoidable weaknesses across interconnected digital environments.
Security testing provides additional insight into how protective measures perform under realistic conditions. Vulnerability assessments, authorized penetration testing, configuration reviews, and recovery exercises can reveal weaknesses requiring attention. Findings should be prioritized according to potential business impact, with corrective actions documented and verified to ensure that identified problems have been appropriately addressed.
Continuous improvement also depends on employee awareness, leadership involvement, and clear security responsibilities. Regular training helps staff recognize common threats and understand how to report suspicious activity. Reviewing incidents, monitoring relevant performance indicators, and updating security policies allow organizations to adapt their infrastructure as business priorities and external threats change.
Future Trends in Cybersecurity Infrastructure
The future of cybersecurity infrastructure will likely involve greater automation, broader cloud integration, and stronger protection for distributed digital environments. As organizations adopt connected devices, remote working technologies, and cloud-native applications, traditional security boundaries become less defined. Security strategies will increasingly emphasize identity verification, continuous monitoring, and consistent protection across multiple platforms and locations.
Another important development is the growing emphasis on software supply chain security and infrastructure resilience. Organizations depend on third-party applications, service providers, and interconnected technology components that may introduce additional risks. Evaluating supplier security practices, maintaining visibility into software dependencies, and preparing for service disruptions will remain important parts of comprehensive infrastructure protection.
Advances in artificial intelligence and cryptographic technology will also influence future security planning. Organizations may increasingly evaluate post-quantum cryptography, automated threat analysis, and stronger protections for machine identities. Successful adoption will require careful testing, professional expertise, and ongoing assessment to ensure that emerging technologies improve security without introducing unnecessary complexity or new vulnerabilities.
Conclusion
Cybersecurity infrastructure plays a fundamental role in protecting modern organizations against digital threats and operational disruptions. It combines network security, endpoint protection, identity management, encryption, monitoring technologies, and established security procedures. Together, these components help safeguard sensitive information, maintain reliable services, and reduce the potential impact of cyber incidents across complex IT environments.
Building effective cybersecurity infrastructure requires more than purchasing advanced security products or implementing isolated technical controls. Organizations must understand their risks, apply appropriate protective measures, train employees, and regularly evaluate their security practices. A layered approach supported by strong access management, reliable backups, and incident response planning provides a practical foundation for long-term digital resilience.
As technology continues to evolve, businesses must adapt their cybersecurity strategies to address emerging risks and changing operational needs. Cloud security, Zero Trust principles, automation, and continuous improvement will remain important considerations. By maintaining a coordinated and risk-based security infrastructure, organizations can better protect their digital assets while supporting sustainable growth and business continuity.
Frequently Asked Questions (FAQs)
What is cybersecurity infrastructure in simple words?
Cybersecurity infrastructure is the combination of technologies, policies, and processes used to protect computers, networks, applications, and digital information. It helps organizations prevent unauthorized access, detect potential threats, and recover from security incidents.
What are the main components of cybersecurity infrastructure?
The main components include firewalls, endpoint protection, identity and access management, encryption, monitoring systems, and secure backups. Together, these measures protect digital resources and support effective threat detection and incident response.
Why do businesses need cybersecurity infrastructure?
Businesses need cybersecurity infrastructure to protect sensitive information, reduce cyber risks, and maintain reliable operations. It also supports regulatory compliance, customer trust, and recovery when security incidents or technical disruptions occur.
What is the difference between cybersecurity and cybersecurity infrastructure?
Cybersecurity is the broader practice of protecting digital systems and information from threats. Cybersecurity infrastructure refers to the specific technologies, controls, personnel, and operational processes used to support that protection.
How can organizations improve their cybersecurity infrastructure?
Organizations can improve security by implementing multifactor authentication, updating software, monitoring networks, training employees, and regularly testing backups. Risk assessments and incident response planning also help identify weaknesses and strengthen long-term protection.

